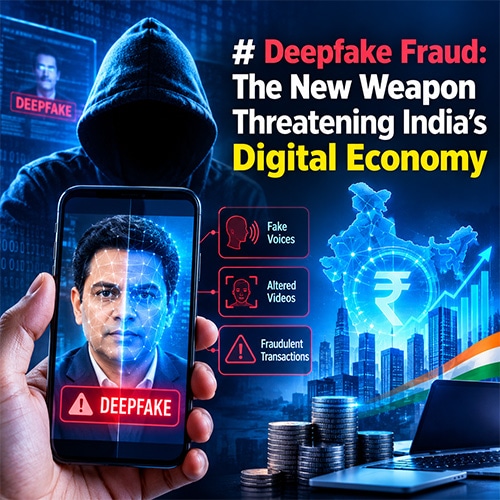
AI-generated voices, synthetic identities and manipulated video calls are turning corporate trust into a cybersecurity vulnerability, demanding urgent action from boards, CISOs and regulators.
A new report by the Trade Promotion Council of India (TPCI) and CyberPeace warns that AI-powered deepfakes and voice cloning are fundamentally transforming India's cybercrime landscape, exposing enterprises to financial fraud, executive impersonation and identity theft.
India's reported cyber fraud losses surged 206%, from ₹7,465.1 crore in 2023 to ₹22,845.7 crore in 2024. Although these figures cover all cyber fraud rather than deepfake-specific losses, they underline the growing financial exposure facing India's digital economy.
Key Highlights:
1. 206% surge in cyber fraud losses: India's reported cyber fraud losses reached ₹22,845.7 crore in 2024, highlighting the broader financial threat.
2. Voice cloning takes seconds: AI tools can reproduce convincing voices from as little as three to four seconds of recorded speech.
3. Executive impersonation threatens enterprises: The Arup and Bharti Enterprises incidents demonstrate how synthetic identities can manipulate financial decisions.
4. Human detection is unreliable: Research indicates that visual and auditory judgment alone cannot reliably distinguish authentic communications from deepfakes.
5. Banking authentication faces new risks: Synthetic faces, cloned voices and injection attacks threaten video KYC, onboarding and account recovery.
6. Multilayered verification is essential: Independent callbacks, dual approvals, behavioral intelligence and advanced detection technologies must work together.
7. Digital trust becomes a boardroom priority: Enterprises need stronger governance, incident response, employee awareness and executive accountability to counter AI-powered impersonation.
The biggest concern is the accessibility of synthetic media technology. Research cited in the report suggests that just three to four seconds of recorded speech can generate a convincing voice clone, allowing criminals to impersonate senior executives and manipulate employees.
According to McAfee research, 47% of Indian adults surveyed reported experiencing AI voice scams personally or through acquaintances. This indicates how rapidly synthetic impersonation is becoming a mainstream fraud concern.
The global warning came from engineering firm Arup, where fraudsters reportedly orchestrated a deepfake video conference that convinced an employee to transfer HK$200 million through 15 transactions. Every participant except the victim was digitally impersonated.
India has already witnessed similar attempts. Sunil Bharti Mittal disclosed that criminals cloned his voice to instruct an executive to transfer funds. Fortunately, the employee questioned the unusual request and prevented the transaction.
The threat extends beyond corporate payments. Banks, NBFCs and fintech companies face synthetic identities designed to bypass video KYC, facial recognition, liveness verification and account recovery mechanisms.
Human judgment alone cannot provide reliable protection. An iProov study cited in the report found that only 0.1% of 2,000 participants correctly identified every genuine and manipulated sample, despite widespread confidence in their detection abilities.
Cybercriminals increasingly combine psychological manipulation, urgency and executive authority with realistic synthetic audio and video. Traditional authentication practices become vulnerable when familiar voices or recognizable faces are treated as sufficient authorization.
The report recommends independent callbacks, dual authorization, behavioral analytics, injection-attack detection and stronger transaction monitoring. It emphasizes that technology must reinforce established verification procedures rather than replace them.
Incident response presents another critical challenge. Organizations must coordinate financial recovery, evidence preservation, regulatory reporting and law enforcement engagement while addressing applicable CERT-In and data protection obligations.
Ultimately, deepfake fraud is no longer merely a content authenticity problem. It represents a direct assault on institutional trust, demanding board-level accountability, multilayered identity verification and a fundamental redesign of how enterprises authorize sensitive transactions.