Artificial intelligence is evolving faster than regulations, governance frameworks, and enterprise policies can adapt.
For Chief Information Security Officers (CISOs), the challenge is no longer preparing for AI adoption—it is managing AI risks that are already entering the workplace through employees, partners, and third-party applications.
As organizations embrace generative and autonomous AI, security teams are struggling to assess new models before they are deployed.
Meanwhile, cybercriminals are leveraging AI to automate attacks, create deepfakes, exploit vulnerabilities, and bypass traditional security controls at unprecedented speed.
This rapidly changing landscape demands a shift from periodic risk assessments to continuous AI security testing.
Organizations need real-time visibility into AI models, data flows, user behaviour, and emerging threats to identify risks before they become security incidents.
Technology alone, however, is not enough.
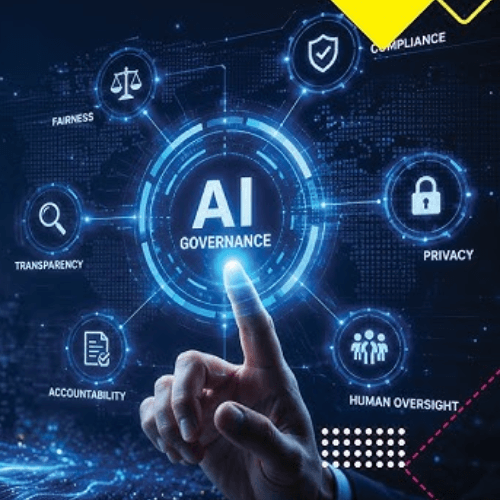
Human judgment remains essential for evaluating AI decisions, ensuring ethical governance, and balancing innovation with risk.
Continuous monitoring combined with expert oversight enables organizations to adopt AI responsibly while maintaining trust, resilience, and regulatory readiness.
For CISOs, governing AI is no longer about waiting for regulations—it's about building adaptive security frameworks that evolve as quickly as AI itself.