
Websense has released the Websense Security Labs Threat Report for the year 2014. It has revealed the latest shift in complex attack trends, evolution in the threat ecosystem and shifting motivation of cyber-attacks.
“Cybercriminals continue to evolve their attack planning and execution to stay ahead of most existing security measures. While the determined, persistent attackers continue to have success in advanced, strategic attacks using zero-day exploits and advanced malware, there has also been a boom in cybercriminal activity on a massive scale. Even these more ‘common’ forms of attack are easily slipping past organizations without real-time defenses,” said Charles Renert, Vice-President of Security Research, Websense.
The Websense Security Labs 2014 Threat Report details the growing global criminal-Infrastructure-as-a-Service economy through exploit kits and compromised websites redirection chains. Through an analysis of the latest attack methodology, Websense security researchers analyze the seven threat stages of advanced attacks. In addition, outcomes include the modification and repurposing of existing malware source code.
Keep reading
Related stories
Security
AI Boom Tests Cybersecurity Stocks
22 September 2026
Security
Sophos: MSPs Are Becoming Acting CISOs for Nearly Half of Their Customers
19 September 2026
Security
Cyble Inks MoU with Cyber Security Council of UAE to Strengthen National Threat Intelligence Capabilities
18 September 2026
Security
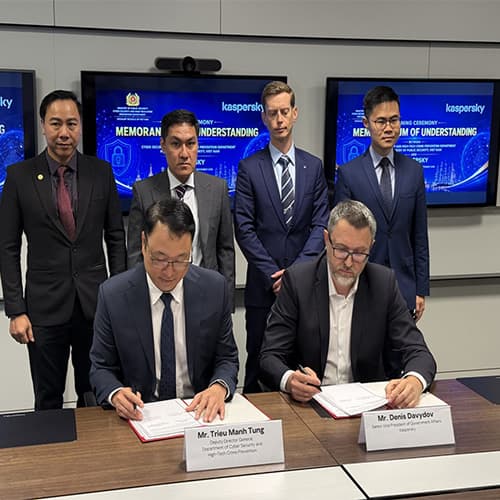
Kaspersky signs MoU with Vietnam’s Cyber Security High-Tech Crime Prevention Department
17 September 2026