
According to a latest report, Websense Security Labs has come across a phishing email targeting customers of Punjab National Bank seeking to obtain password credentials of corporate as well as individual customers.
This phishing campaign requires the recipient to open an email attachment and fill in the required fields including: user ID, Password, transaction password and mobile number. Once completed, the form redirects customers to the legitimate bank site while their personal information including password credentials are sent to a server under the attacker’s control.
Websense has also announced that it has taken measures to proactively block this phishing campaign using ACE (Advanced Classification Engine) at multiple stages of the attack chain.
Keep reading
Related stories
Security
Sophos: MSPs Are Becoming Acting CISOs for Nearly Half of Their Customers
19 September 2026
Security
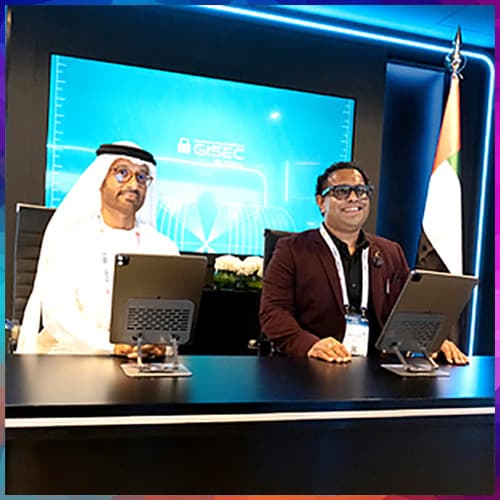
Cyble Inks MoU with Cyber Security Council of UAE to Strengthen National Threat Intelligence Capabilities
18 September 2026
Security
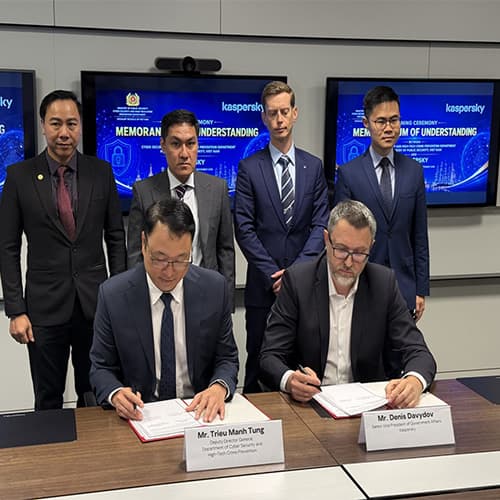
Kaspersky signs MoU with Vietnam’s Cyber Security High-Tech Crime Prevention Department
17 September 2026
Security
Indian SMEs step up cybersecurity investments as threats evolve
16 September 2026