
According to statistical data compiled by Dr.WEB regarding one of the widespread threat Trojan.Mods.1, it has been revealed that the number of infections with this Trojan represent 3.07% of the total number of detected threats.
Trojan.Mods.1 is chiefly designed to replace web pages visited by users with malicious web pages by intercepting the system functions responsible for translating DNS names to IP addresses. As a result, instead of the sites they have requested, users are redirected to fraudulent pages where they are asked to enter a mobile phone number and reply to an SMS sent from the short number 4012. If they comply, a certain amount will be debited from their account.
This threat has been designed containing a special algorithm that allows redirection to a certain group of addresses to be disabled.
The configuration file containing all the data needed to run Trojan.Mods.1 is encrypted and stored in the dynamic linking library. The signature of this threat has been added to the Dr.WEB virus database, to make sure that Trojan.Mods.1 does not pose a serious threat to systems protected by Dr.WEB 's products.
Keep reading
Related stories
Uncategorized
ATL SOC in CrowdStrike platform provides security for evolving threat landscape
6 November 2025
Breaking News
Alibaba unveils China's most powerful AI chip ahead of Xi-Trump summit
23 September 2026
Breaking News
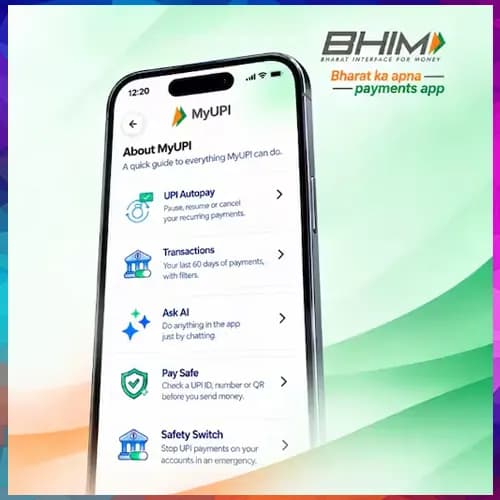
NPCI launches AI chat assistant 'MyUPI' on BHIM app for payment support
23 September 2026
Breaking News
Trai mandates voice-and-SMS-only tariff plans to aid low-data users
23 September 2026